130+ years across law, AI, enterprise software and finance

130+ years across law, AI, enterprise software and finance

Talk to our counsel

ABOUT INDISEC

Compliance is a legal outcome, not a software feature.

Compliance is a legal outcome, not a software feature.

Compliance is a legal outcome, not a software feature.

We build agents that carry the volume of privacy work, and we put lawyers in the seat where judgement is required. Both halves matter. Most tools in this category only have one.

We build agents that carry the volume of privacy work, and we put lawyers in the seat where judgement is required. Both halves matter. Most tools in this category only have one.

We build agents that carry the volume of privacy work, and we put lawyers in the seat where judgement is required. Both halves matter. Most tools in this category only have one.

WHY NOW

Indian enterprises inherited obligations without an operating system for them

Indian enterprises inherited obligations without an operating system for them

Indian enterprises inherited obligations without an operating system for them

The Digital Personal Data Protection Act made every organisation that handles personal data a Data Fiduciary, with duties that do not scale on good intentions: know what personal data you hold and why, collect consent you can actually evidence, answer a Data Principal inside a deadline, and notify a breach without waiting for certainty.

The Digital Personal Data Protection Act made every organisation that handles personal data a Data Fiduciary, with duties that do not scale on good intentions: know what personal data you hold and why, collect consent you can actually evidence, answer a Data Principal inside a deadline, and notify a breach without waiting for certainty.

The Digital Personal Data Protection Act made every organisation that handles personal data a Data Fiduciary, with duties that do not scale on good intentions: know what personal data you hold and why, collect consent you can actually evidence, answer a Data Principal inside a deadline, and notify a breach without waiting for certainty.

Most of that work currently lives in spreadsheets, email threads, and the memory of whoever set it up. It holds until the first regulator letter, the first deletion request, or the first diligence questionnaire. Closing that gap is why IndiSec exists.

Most of that work currently lives in spreadsheets, email threads, and the memory of whoever set it up. It holds until the first regulator letter, the first deletion request, or the first diligence questionnaire. Closing that gap is why IndiSec exists.

Most of that work currently lives in spreadsheets, email threads, and the memory of whoever set it up. It holds until the first regulator letter, the first deletion request, or the first diligence questionnaire. Closing that gap is why IndiSec exists.

HOW WE WORK

Agents for volume. Lawyers for judgement.

Agents for volume. Lawyers for judgement.

Agents for volume. Lawyers for judgement.

Agents do the sweep

Agents do the sweep

Agents do the sweep

Discovery across your systems, classification of whatever turns up, and continuous tracking of the obligations that attach to it. This is the work that defeats a quarterly spreadsheet.

Discovery across your systems, classification of whatever turns up, and continuous tracking of the obligations that attach to it. This is the work that defeats a quarterly spreadsheet.

Lawyers own the call

Lawyers own the call

Lawyers own the call

Where a judgement is required - is this a reportable breach, is this consent valid, is this use legitimate - a qualified lawyer decides. Not a model, and not a checkbox.

Where a judgement is required - is this a reportable breach, is this consent valid, is this use legitimate - a qualified lawyer decides. Not a model, and not a checkbox.

You keep the evidence

You keep the evidence

You keep the evidence

Every decision lands in a register you can hand to a regulator, an auditor, or an acquirer, with the reasoning attached to it.

Every decision lands in a register you can hand to a regulator, an auditor, or an acquirer, with the reasoning attached to it.

Our leadership

Prateek Som

Co-Founder & Legal Advisor

17+ years in law, governance and public policy. Harvard and NLU Delhi; former Standing Counsel, Government of Haryana; an authority in technology law, data privacy and regulatory strategy.

Anup Bhasin

Co-Founder & CEO

35+ years leading global businesses across American Express, Standard Chartered, IBM Daksh and UnitedLex. A lawyer, Fellow Chartered Accountant and Certified Internal Auditor who has scaled start-ups into profitable ventures.

Abnesh Raina

Co-Founder

20+ years in AI, analytics and enterprise technology. Harvard and Columbia; former CIO of B/E Aerospace, where he built technology assets later acquired by Boeing; founder of multiple ventures.

Anita Sharma

Chief Data & AI Leader

20+ years in enterprise data and AI, including as a Data Strategy leader at Salesforce, Oracle and DHL, spanning enterprise data, AI/ML, governance and digital transformation.

Naveen Kapoor

CFO

Chartered Accountant with 30 years’ experience in fundraising, M&A, investor relations and governance across Sirion Labs, UnitedLex, IBM Daksh and Business Standard.

Shourya Magotra

VP, Technology & Product

12+ years in AI and product leadership. Trained in Data & Decision Science at IIT Delhi and AI for Business at Wharton. Holds multiple AI/ML patents and builds IndiSec’s AI-powered compliance products.

130

+

years’ collective experience across legal and regulatory strategy, AI and data science, enterprise software, finance, governance, fundraising and scaling global businesses.

Data privacy professionals

Aparna Mitra

Privacy & Data Protection Lead

10+ years advising global clients on GDPR, DPDPA, HIPAA and CCPA compliance frameworks. Previously a Legal & Compliance Consultant at EY, leading privacy risk assessments and third-party due diligence.

Ankur Singh

Privacy & Compliance Counsel

A data protection lawyer advising organisations on GDPR, CCPA, PIPEDA, PDPL and the DPDP Act, operationalising consent systems and cross-border data transfers.

Sanjhi Sharma Garg

Data Privacy Professional

A Gold Medalist LL.M. in Business & Corporate Laws with 4+ years at Shardul Amarchand Mangaldas, DSK Legal and Khurana & Khurana. Specialises in the DPDP Act, GDPR and comparative frameworks.

Saumya Singh

Data Privacy Professional

An LL.M. in Telecommunications, Media & Technology Law from Symbiosis Law School, with 2+ years across GDPR, CCPA and the DPDP Act. Drafts privacy notices, retention policies and breach response frameworks.

Sunaina Jain

Data Privacy Professional

5+ years across litigation, regulatory research and data protection, including as a Data Breach Reviewer at Elevate Services on GDPR, HIPAA and IT Act matters. NALSAR-trained in data protection law.

Advisory board
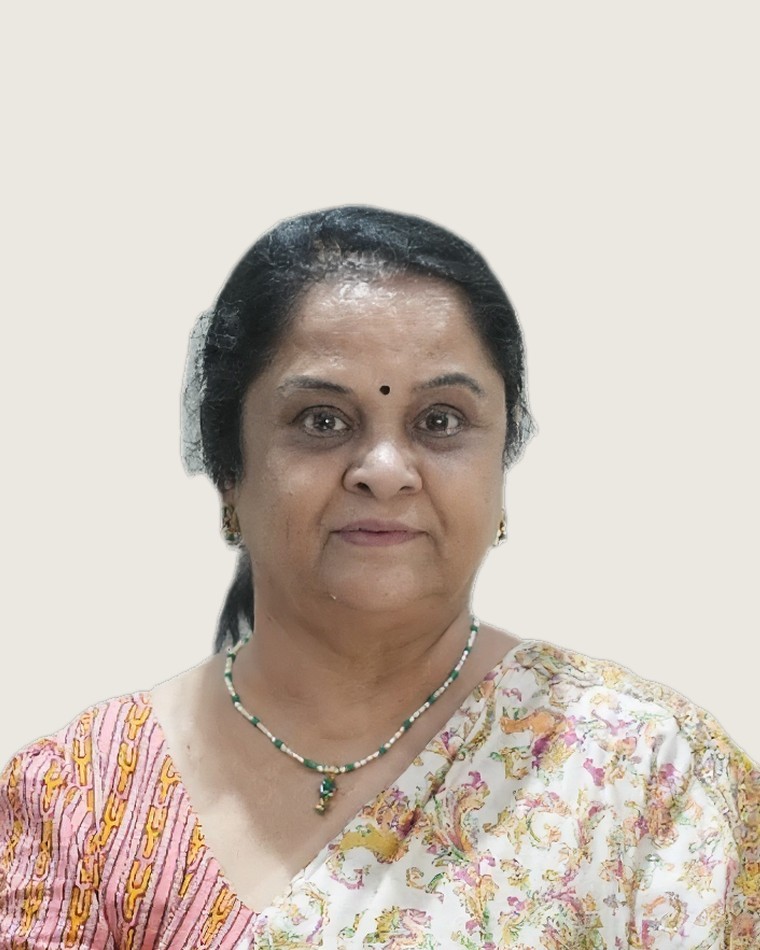
Dr. Aruna Sharma

Advisory Board Member

A development economist and former Secretary to the Government of India (Ministry of Electronics & IT and Ministry of Steel). Serves on the RBI’s High-Level Committee on Deepening Digital Payments in India.

Meet the people who govern every gate.

Certified counsel, technologists and operators stand behind every agent action, from assessment to evidence.

Talk to our counsel